Historical website restoration from a legitimate Wayback Machine capture. Archived actions are inactive.

Contents and Sample Chapter
Contents

HomeIntroductionReviewsToolsUpdatesPurchaseContact

Table of Contents


Introduction:
Separating fact from fiction regarding firewalls and their security limitations; the security advantages of using open-source applications on Windows; installing the free, open-source Mozilla Web browser and e-mail client, and configuring them for maximum security and online privacy to escape numerous problems inherent to Internet Explorer and Outlook Express
Intro

Ch 1, Introducing the Dark Side:
Exposing the embarrassing truth about malicious hackers and why you need not be afraid of them; why the media promote hacker mythology while ignoring the reality of system weaknesses brought about by poor software design and bad default configurations; the ease of frustrating the vast majority of script kiddies with sensible system configurations.
Script kiddies

Ch 2, Vectors:
Understanding malware, spyware, bad system configurations, and the scores of other routes to system exploitation and privacy invasion that firewalls and antivirus software don't address; a step-by-step guide to simplifying and hardening a system, turning off dangerous and unnecessary networking services, and setting sensible user permissions, liberally illustrated with screen shots.
Vectors

Ch 3, Social Engineering:
Recognizing the many scams used by malicious hackers, spammers, and similar online vermin to trick users into taking action such as opening a malicious file or following a link to a malicious Web site; spotting the signs indicating scam e-mails and other forms of manipulation; developing the habits of defensive computing and defensive Web surfing.
SE

Ch 4, From Newbie to Power User:
Learning to take full control of your computer; a step-by-step guide explaining how to monitor an Internet connection to spot software secretly reaching out or phoning home to remote servers; how to monitor your system for signs of malicious processes; and how to use PGP and GPG to encrypt your sensitive files and Internet correspondence, liberally illustrated with screen shots.
Taking control

Ch 5, Treasure Hunt:
How to eliminate all traces of Web activity from your computer and defeat forensic recovery of stored data; how to prevent your computer from collecting such data in the first place; how to surf the Web anonymously using an encrypted connection and defeat remote monitoring; how to set up and use SSH (SecureShell) and anonymous proxies to conceal both your identity, and the data content of your Internet sessions, from all third parties, including your ISP.
Data hygiene

Ch 6, The Open-Source Escape Hatch:
Understanding the advantages and disadvantages of migrating from Windows to Linux; why Linux is easier to configure for security, and why it's better suited to less technically-inclined users; how to judge whether Linux is right for you, and the issues you should consider before migrating.
Linux

Ch 7, Trust Nothing, Fear Nothing:
Exposing the exploitation of mythology and fear by the security and antivirus rackets; how to think about security and evaluate your own security needs; recognizing threats that are real and ones that are legendary; taking control of your own security and privacy; and learning to be skeptical at all times, but never afraid.
Detecting FUD


Appendix A, Glossary

Appendix B, Procedures, Processes, and Ports:
Notes on NAT
Notes on Packet Filters
Windows Processes
Ports

Appendix C, Online Resources:
Security News
Resources
E-mail Lists

Preface

This is a handbook for ordinary people concerned about computer security and online privacy. It addresses everyday computer users and Netizens with little or no background in information technology, concerned parents, business users, and corporate telecommuters. It involves both theory and practice: readers will learn the most common techniques used by malicious hackers, spammers, identity thieves, online marketers, and Internet fraudsters, and receive detailed instruction to defend their systems against exploitation, protect their privacy and avoid identity theft.

Whether one uses a desktop or workstation connected to a professionally managed network on the job, a single computer connected to the Internet at home, or a small network serving both business and personal needs and accommodating several users, including children and teenagers, the basic approaches remain the same. No special skills are needed: anyone can understand and adopt the essential habits of computer security, data hygiene and online privacy. If you can use a computer or workstation, log on to the Internet or a company network, use an instant-messaging or chat client like ICQ or AIM, a Web browser, a search engine, and an e-mail client, then you can learn to use them safely, even anonymously. This book will show you how.

There is an air of myth surrounding cybersecurity and the hacking underground, one vigorously encouraged by celebrity hackers seeking to distinguish themselves, and by security and antivirus vendors who profit by promoting the fiction that only professionals dare confront the inscrutable denizens who lurk in the seedier districts of cyberspace. Today, computer and network security are extremely valuable territorial possessions belonging to highly trained, and highly paid, specialists, just as French haute cuisine was in the 1960s, before an ordinary housewife named Julia Child demystified and simplified it for the home cook. The analogy is a good one: just as the supposed mysteries of French cookery come down to a theoretical framework and a set of techniques that anyone can master, so does defensive computing. It is not rocket science; it is in fact almost entirely a matter of common sense. True, there is a theoretical framework and there are techniques, but these, just like a recipe for pate feuilletee or coquilles Saint-Jacques, can be understood and mastered by anyone willing to learn.

Whether you're a home user concerned about software bugs and viruses, commercial profilers, identity thieves, and malicious hackers on the Internet; a parent worried about your children's exposure to online perverts, pornography, and mindless hate speech; or a corporate security manager struggling to communicate the rationale of network security to your nontechnical but wired staff, you'll find this book a faithful companion, one that will debunk the myths of security and cybercrime and offer instead realistic warnings, clear background explanations, and patient, step-by-step tutorials with a minimum of technical jargon.

The book is meant to be read through, not flipped through, because security is a cumulative process with many interdependent layers. Some chapters are devoted to practical steps for hardening systems and assuring privacy and Internet anonymity; others are more concerned with background and theory. I've tried to present these elements in an interlaced order that makes the whole easier to grasp, rather than adhere to some rationalistic scheme such as a textbook might follow. The twin elements of theory and practice must both be considered before good decisions can be made. Similarly, security and privacy must be applied together: it's impossible to harden a system without good privacy protection and data hygiene, yet privacy can't possibly be assured on a soft system. I'm separating these elements into digestible bits and arranging them in a more natural sequence to make them easier to grasp, but they all work together and need to be applied in an integrated manner.

You will encounter tutorials with detailed procedures throughout the book, starting with the Introduction, and these can be applied at any time to advantage. But it's better to read through and get a sense of the larger picture before carrying out the instructions because something you learn in Chapter 6, say, might affect your approach to a tutorial back in Chapter 4. While I'm loath to discourage tinkering, an initial read-through will help you avoid backtracking and duplicating your efforts. Generally, the practical information -- the 'what to do' guidance -- comes first, and the background information -- the 'what to know' guidance -- comes later. The book is loosely structured that way, and most chapters are as well.

Because this book is written primarily for home and small business users, and desktop users in the corporate world, when we talk about Windows we'll focus on the user-friendly Windows XP for our practical examples, though these should be easy for users of Windows NT and Windows 2000 to adapt to their systems. Similarly, UNIX-related tips will be based on GNU/Linux, which is popular in home and small business environments, though UNIX and BSD users should not have difficulty adapting them to their systems.

Because Windows represents the majority of installed systems among likely readers of this book, I will naturally be giving it more attention than Linux, but the basic principles of security and privacy are fairly universal, so Linux users can certainly benefit from material addressed to Windows users. And of course there will be Linux-specific material throughout the book, including a chapter detailing its numerous advantages for the security-conscious user, and in particular, the novice.

One of the more controversial tenets of this book, though one that will be proved handily, is that Linux is better suited than Windows to the security novice. This might seem counterintuitive now, but it will gradually become evident that the procedures for securing Windows are more complicated, more numerous, and less effective than those for Linux. As recently as two years ago, Linux was difficult to install and use, but great strides have since been made in accommodating novices, especially by the big vendors such as SuSE and Mandrake. Users who want the best computer security with the least bother and expense will be better served by Linux. But Windows enthusiasts need not despair; Windows XP can indeed be configured for improved security. It's not at all difficult, but it is more involved than securing a Linux system.

It will sometimes be necessary to use technical terms in passing that will be explained in later chapters. Readers need not be concerned if a term or concept seems unfamiliar when it's first introduced; as you progress through the text, your knowledge will broaden and the context will deepen, as one chapter illuminates another. Readers will gradually become conversant in the peculiar lingo of systems vulnerabilities and the tools and techniques used to control them, though in Appendix A there is an alphabetical glossary of all technical terms, jargon, and acronyms used in the book. Expressions that might be unfamiliar are italicized when first mentioned as a reminder to consult the glossary, but patient readers can rest assured that all mysteries will be explained in due course.

Despite what you may have been led to believe, security is not a black art and the Internet is not some spooky realm of pure evil like the enchanted forest in which Hansel and Gretel nearly met their doom. Risks can be managed, systems hardened, and hackers and privacy invaders frustrated. There is no reason to be apprehensive, though there is reason to be both cautious and skeptical. Computer security is not rocket science: you can learn it, and you will.

Introduction

The magic of firewalls

There is perhaps no piece of security equipment more shrouded in superstition than the firewall. It's a familiar item, though poorly understood, likely to be the first thing most people think of when computer security is mentioned. Almost everyone, regardless of skill level, talks about them, recommends them, and secretly worries that theirs might not be quite up to the task. Many home users have one whether they know it or not, either in the form of a small router for connecting several computers to a single modem, or in the form of a software program like BlackIce Defender or ZoneAlarm, which are called packet filters or personal firewalls.

Indeed, there is much that a firewall can do to improve security, but there is also a great deal that it can't. Many users, even many IT managers, erroneously imagine it to be a panacea of network and Internet security. A firewall does not create the equivalent of a digital bunker within which we're safe from attack. In truth, it addresses only a small, though important, set of vulnerabilities. Relying on a firewall for general security is very much like relying on a locked door at home when the windows are open. There are scores of routes by which a computer or a network can be attacked and compromised, both remotely and locally. Firewalls defend against only a fraction of them.

In its basic form, a firewall is a physical device. This type can be as simple as a NAT (network address translation) router for home users, such as the popular Linksys and Netgear cable/DSL broadband routers sold at retail for $100 or so, or as elaborate as an entire computer system loaded with various types of software for commercial users costing tens of thousands of dollars. Either way, a firewall is essentially a separate box that sits between your computer and a network, or your local network and another, larger one such as the Internet.

NOTE: NAT routers are relevant to broadband users who connect to the Internet with an internal Ethernet card rather than a telephone modem. Dialup Internet users who connect with a standard phone modem can install a packet filter, or personal firewall, instead.

This physical buffering is useful because when you make an Internet connection through a router-style firewall, the traffic you generate appears to originate from it and the traffic you receive appears to end at it. This makes it difficult for the many unsophisticated would-be hackers called script kiddies populating the Internet to locate your computer. When a computer's location can't be pinpointed, a number of attacks become awkward for the vast majority of mediocre, wannabe hackers to mount. Of course, to a sophisticated attacker with a thorough grasp of software programming and network protocols, a basic firewall is little more than a speed bump. For this reason, firewalls used in defense of corporate networks contain a great deal of added capability and may be custom designed, generally at great expense.

There are four basic types of firewalls, but only the first two are relevant to home users:

Packet filters: These are software programs running on a client machine such as a PC. On an Internet-connected PC, they block access to particular ports behind which insecure services may be running. They are commonly used on home systems, particularly by dialup users for whom a router would be superfluous. Most are inexpensive and quite effective.

Circuit proxies: These are physical boxes that create a gateway through which a computer connects to a network or the Internet. They forward data between the computers they're protecting and the network, and hide the IP addresses of each user's PC. Circuit proxies are physical buffer zones: they establish their own IP address on the Internet, then assign internal IP addresses that are not Internet-routable to each machine they're defending. A NAT router is an example of a circuit proxy for home systems using a broadband Internet connection.

Application-layer firewalls: Unlike a routing firewall, such as a circuit proxy, these actually stop and filter network traffic, examine it for malicious content, then forward it to the host if the traffic or request is legitimate. They are used on host systems such as servers. They examine traffic for malicious code and malformed packets meant to attack specific applications on the host system. Generally, they are designed to protect only a single application that cannot be blocked, such as the Apache Web server, and are therefore used in combination with other, more general defenses. A good one will eliminate malicious traffic related to individual application vulnerabilities, but the chief drawback is a fair bit of computational overhead that can slow system performance.

Swiss Army knives: There are security appliances that claim to combine the benefits of routing and proxying, flood protection, application-layer filtering, intrusion detection, encryption, and more. Often they carry additional costs from required support services and impose a significant performance drain. Their added complexity is itself a security issue. And remember, a Swiss Army knife may be invaluable when nothing better is available, but it really doesn't do anything terribly well. Always beware of any security pitch promising a catch-all panacea. If it "slices, dices, chops and grates," it probably won't handle any of those tasks with much grace.


Home users with dialup connections are quite well served by a good packet filter. For the Linux home user with a broadband connection and no Internet servers, a simple, hundred-dollar NAT router is perfectly adequate. Windows home users with a NAT router also need a packet filter capable of egress filtering, which we will learn about in the following section. For an office or small business network with no Internet servers but client PCs with both local network and Internet connections, there are routers or circuit proxies with added capability in the $200 to $500 range that will usually prove adequate, especially if a packet filter is installed as well.

Of course, when you offer services over the Internet, firewalling gets more complicated. However, we won't be getting into server-side security because plenty of resources already exist. Our concern is securing the client system, whether a stand-alone PC or home network, or a thousand desktops in a business environment, because this is an element of computer security that has received too little attention. Remember, a single insecure client program can open a home PC to remote exploitation in spite of diligent defensive efforts, and even undermine thousands of dollars worth of professional security services and equipment in the workplace.

Home and small business users should beware of overspending on firewall products. A bank or corporate network contains assets valuable enough to attract the cleverest of blackhat hackers. Attacks against such targets are expensive in terms of time and effort, but the goal is well worth it. By comparison, the home PC and small business network are insignificant targets for an elite blackhat, but are often sought by script kiddies looking for credit card data or seeking to commandeer a number of machines for launching DDoS (distributed denial of service) attacks and similar nuisances. A simple packet filter or router-style firewall is an important element in making attacks against a home or small business system too expensive for the mediocre intruders it tends to attract.

Any good, inexpensive firewall should be capable of stateful packet inspection (SPI), a routine in which packets destined for any port not in use will be dropped, but where ports the user activates will be opened automatically. Packets are the basic units of data exchanged over the Internet. E-mail memos, instant messages, even the Web pages that show up in our browsers, are a function of packets, or datagrams. When a large chunk of data is sent, it's broken into several packets for ease of transport and reassembled at the destination. A port is a logical structure, not a physical opening, but it can be imagined as a virtual opening through which data packets flow both out of and into networked computers. Ports are numbered sequentially, and there are standard ones enabling particular applications, servers, and clients to communicate with each other across a local network or the Internet.

Let's look at a familiar example. When you click on a hyperlink or type a URL into your browser's address field, your PC communicates with a remote Web server and asks to be sent the contents of a particular Web page via a protocol called HTTP (hypertext transfer protocol). In order to make the request, your browser, acting as a client, opens a port on your computer and exchanges several small packets with the server in a routine called a handshake to establish a two-way connection, or session. The Web server, acting as a host, is listening on port 80 for just this sort of initial request and is programmed to answer it. After a brief handshake, a session is established and the data you've requested is sent to your computer in several packets to be reassembled as a Web page in your browser.

NOTE: The words client and host can be confusing. A client is a machine or an application, such as a browser, that requests a service, and a host is a system, such as a Web server, that offers a service. We think of the PC as primarily a client system reaching out for services offered by host systems, but it also makes services available, and in so doing sometimes functions as a host as well as a client. To further confuse everyone, any device connected to a network may be referred to as a host.

We'll learn the actual nuts and bolts of how one computer interacts with others in later chapters; for now, the important thing to note is that the Web server is available on a particular port and is designed to accommodate requests for any services it's offering that have been sent to it through that port.

Home computers, especially Windows computers, have a great number of open ports because Windows is designed with a tremendous amount of networking capability that's installed and enabled by default. Much of this capability is superfluous to Internet users, and some of it is actually dangerous, being meant for use only on a trusted network, not the Web. These extra functions leave us exposed on the Internet. If someone happens to be scanning the Net for vulnerable machines and pings yours on the right port, your computer will answer. You likely have several services running on your PC, all listening for requests on their respective ports. If they're pinged, they'll respond. This is how malicious hackers and script kiddies find your machine on the Internet.

Without a firewall or packet filter, your computer will respond to packets sent from anywhere on the Internet. If you have a firewall capable of stateful packet inspection, it will automatically drop any packet destined for a particular port on your computer when that port is inactive. A simple firewall or filter will block incoming connections to particular ports, but stateful packet inspection allows your firewall to open a port automatically when you want to use it, and close it automatically when you're done. It records the state of a connection and recognizes connections you've deliberately made. This prevents your computer from responding to probes from machines with which you haven't established a connection, while allowing machines with which you've deliberately established a session to contact you.

For example, let's say that you have an active browser connection with a remote machine at the IP address 123.1.1.1. When stateful packet inspection is active, only packets originating from that IP address will be forwarded to your computer by the firewall. A packet sent from any other location on the Internet will be ignored, even though your browser is active and listening for data.

On the server side, stateful packet inspection can defeat some denial of service attacks by recording the origin and state of packets sent to the host machine. If packets start arriving from a remote location, yet no connection or session is ever established, the firewall will remember this and automatically ignore additional contacts from that location, and therefore not waste system resources trying to accommodate bogus requests.

This is all good because it's common for malicious script kiddies to scan the Internet looking for unprotected computers, servers, and networks. They use automated port scanners capable of searching large swaths of the Internet, automatically sending packets to chosen IP addresses port-by-port. For example, such a tool might be configured to scan the IP range 123.1.1.1 to 123.1.1.100. The program will ping, or send a packet to, each port at each IP address in turn. It might begin by pinging 123.1.1.1 port 21 (FTP), then 23.1.1.1 port 22 (SSH), then 123.1.1.1 port 23 (Telnet), and continue in this manner until the entire list is exhausted.

Most script kiddies are mere opportunists searching for vulnerable machines, much like a thief trying doors in a hotel corridor. A locked room is usually all that's needed to discourage this type of attack. Most thieves will simply move on, looking for an unlocked, unoccupied room. In a very broad sense, stateful packet inspection is similar to locking your hotel room from the outside, but not from the inside. You can open the door whenever you please, to whomever you please, but others can't. Your computer can have an open connection, or several of them using a number of different clients and services, yet your firewall will drop any packet that arrives from an address that does not correspond to one of the connections you've made.

Suppose you have an active connection with a server at 123.1.1.1 and a packet arrives from a kiddie scanner at a completely different IP address, say 123.2.2.2. The packet will be dropped by the firewall because you do not have a connection established with that address. To the script kiddie using the scanner, there will be no reply and it will appear that there is no computer at your IP address.

So, what if your router doesn't support stateful packet inspection? Should you run out and buy a new one? Definitely not; in this case you can install a personal firewall or packet filter to create an additional line of defense. Windows users with simple, router-style firewalls can use products like Tiny Personal Firewall, BlackIce Defender, ZoneAlarm, or Sygate Personal Firewall, which are all easy to handle. Linux users can install IPchains for the 2.2.x kernel and IPtables for the 2.4.x kernel. These Linux packet filters are difficult for novices to configure manually, but there is a user-friendly frontend called Bastille which will configure packet filtering and also tighten other security elements, such as file permissions and the like.

A simple NAT router, used at home to connect several PCs to a single broadband Internet connection, serves quite well as a firewall. If you're using one, it's important to know whether it supports stateful packet inspection: some do and some don't. If it doesn't, you can deploy a packet filter to extend its capability. If you're using a dialup connection, you won't be using a NAT router, so you definitely need a packet filter or personal firewall capable of stateful packet inspection.

Firewalls and packet filters are important, but there is a great deal they can't do. While they may accept outside traffic only when you have an active connection, they can't determine whether you made the connection voluntarily or a malicious program running without your knowledge made it on your behalf. If someone sends you a malicious program via e-mail or instant messaging, or by enticing you to download it from a Web site, it may establish a connection to the Internet without your knowledge. To a firewall, these connections are no different from ones you make voluntarily. Thus a stranger can easily connect to your PC remotely, right through your personal firewall or your company s very expensive professional firewall. It happens every day.

Some packet filters will pop up an alert message, warning users whenever a program installed on their PC attempts to contact the Internet. This is called egress filtering, and it's one way of dealing with spyware and other malicious programs hidden on your machine. Egress filtering is a very useful feature that can alert you to the presence of malware, and it's important to know that Microsoft's Internet Connection Firewall, shipped with Windows XP, does not yet offer it. It performs ingress filtering only. If a malicious program hidden on your PC were to make a connection to the Internet, the standard Microsoft firewall would allow it to do so without warning you. Thus egress filtering, like stateful packet inspection, is an important feature that one should look for in any firewall product. And it's not expensive. You can buy a router capable of stateful packet inspection and a packet filter capable of egress filtering for about $100.

All Windows users, regardless of how they connect to the Internet, need a packet filter capable of egress filtering. There is too much phone-home capability built into Windows itself, and into the applications it runs, for a user to depend on a router alone, even with SPI. It is essential that outbound connections be monitored.

Egress filtering is good, but it's hardly foolproof. If a malicious program is given a familiar name or is integrated into a familiar program, users may not realize that they need to block it when it attempts to connect to the Internet. For example, one particularly stealthy piece of spyware from SpecterSoft, called eBlaster, records a user's every keystroke, including their passwords, every Web site visited, and the contents every online chat and every e-mail sent and received. It then silently forwards all this data to the e-mail account of a remote spy. The eBlaster program is difficult to detect because it integrates itself with the familiar Windows shell, Explorer. When eBlaster runs for the first time, packet filters capable of egress filtering like ZoneAlarm will alert the victim with a popup, warning that Windows Explorer (explorer.exe) is attempting to connect to the Internet. But because Explorer is such a familiar program, and because it normally phones home to Microsoft when the Windows Search Assistant is activated, users may believe its activity to be innocent and permit it to connect when eBlaster invokes it. (For additional information about egress filtering, see Appendix B.)

Another thing that no firewall can do is shield your identity from the Web sites you visit. It cannot deter commercial profilers and spammers. It cannot protect your privacy or anonymity on line. It cannot defend you against spyware and viruses, except marginally if it performs egress filtering. It cannot eliminate insecure clients and services running on your computer; it merely blocks or conceals them. It cannot secure your machine against unauthorized action taken by local users. In short, a firewall does not make your PC more difficult to attack. It only blocks certain ports associated with insecure clients and services, if used properly, and makes your computer more difficult for remote attackers to locate on the Internet. That's all good, certainly, but it's only the tip of the iceberg.

"Hackproofing"

By the time you've finished reading this book, you will indeed be able to "hackproof" your computer, company workstation, home network, or small business network. By hackproofing I do not mean making your system an impenetrable bunker; nothing can do that. Instead, I mean using common sense and layers of protection to make compromising your system more trouble than it's worth. This involves a doctrine called defense in depth, which is based on three general principles that we will learn in detail:

Prevention: Reducing your target footprint through firewalling, keeping a low profile on the Internet, patching software and operating system vulnerabilities, and declining to open e-mail attachments and other risky files.

Resistance: Setting sensible file and user permissions, disabling unused services and daemons, and installing reliable software -- in other words, hardening the system.

Tolerance: Securing the private data stored on your PC and your personal communications via e-mail and chat clients against interception or access by remote attackers and local snoops (e.g., nosy housemates), and encrypting and backing up crucial data, thereby limiting the damage that a system compromise or other security snafu can cause.


Those are the three elements of defense in depth, or effective computer security: prevention, resistance, and tolerance. Unfortunately, there is no magic bullet. Regardless of what the marketing departments of security and antivirus vendors might lead you to believe, there are unknown threats that no one can defend against; therefore it is impossible to make a computer or network totally and literally "hackproof." Internet service providers and software vendors like to give the impression that whatever they have to sell will make us safe, but this is mere marketing hype.

For example, the MSN-8 television ads from the spring of 2003 with the slogan "it's better with the butterfly" show an actor in a killer-bee costume dutifully shielding a mother and her small children from nasty bits of life on the street, implying that one need only switch one's ISP (internet service provider) to MSN and all will be well. In fact, Microsoft Windows, MSN, Hotmail, and Microsoft Passport are all notoriously buggy. Hotmail's spam filters are among the weakest in commercial use. Exploits against Hotmail and Passport surface regularly, and exploitable Windows bugs are reported at a rate of roughly one a week. Indeed, during the time when the TV ad was running, Microsoft was forced to sue a number of bulk spammers precisely because its technical solutions have been a failure.

AOL is guilty of the same marketing hype, touting its automatic McAfee virus scanning feature as a veritable panacea of online security. If you want your computer to be able to play with other computers without getting sick, get AOL for broadband with automatic virus protection, the advertising copywriters urge. Virus scanning is indeed a useful tool, but it's hardly adequate to prevent computers "getting sick."

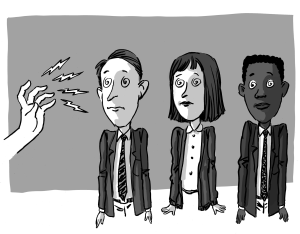
Cisco Systems also joined the security-based advertising carnival with a TV ad showing a group of hipster "international hackers" tearing out their hair in frustration while trying to own the network of a Cisco customer. The scene then moves to a group of clueless Yuppies in suits on the other side of the equation, marveling at their presumably impenetrable Cisco server. "It's got self-protective features," one remarks with much awe and little comprehension. The others nod in deference to Cisco's magic technology, unwilling to speak lest they offend the mysterious pixies and sprites responsible for this feat of security sorcery.

None of these vendors actually claims that their gimmicks and slogans add up to invulnerability, however, and with good reason: Oracle CEO Larry Ellison made that mistake in November of 2001 and soon came to regret it. During his keynote speech at the Comdex technology conference in Las Vegas, Ellison stated flatly that Oracle is "unbreakable." Security researchers David and Mark Litchfield of Next-Generation Security Software (NGSS) then spent the better part of the next 18 months publishing exploit after exploit against Oracle in a seemingly endless and humiliating series. Ellison was soon forced to rewrite history, suggesting that he'd meant "unbreakable" in the sense of "relatively difficult to break," not in the sense of impossible to break. So much for unbreakable products. No one will repeat Ellison's blunder in public again, but so long as computer and network security remain popular issues, vendors and their marketing copywriters will urge us toward the belief that their products offer a unique safety advantage. And they may indeed offer one; only what's needed is a comprehensive approach, not any particular gimmick.

Security is not a product you buy; it is not a gizmo you bolt on to your server rack; it is not a service you subscribe to. It is a process: one that begins with good information combined with common sense and skeptical thinking. And that doesn't mean just being skeptical of the claims of vendors; it means being skeptical of your own habits, your own equipment, your own software. The risks can never be eliminated, but they can be managed quite well. The more you know, not just about what you can do to defend yourself, but also about what you can't do, the better equipped you'll be to make wise choices whenever you're using a computer.

An Open-Source Solution


Microsoft Windows is far and away the most popular desktop operating system and far and away the least secure. There are many reason why this is so. For one thing, Windows wasn't developed with Internet security in mind; the Net wouldn't become popular until near the end of the Windows 3.x development cycle, by which time the operating system was well established. The first retail edition for desktop users with Internet use in mind, Windows 95, was filled with 3.x legacy code and based on extremely naive assumptions about the security implications of the Internet, which had been engineered as a convenient way to transfer data, not protect it.

The Internet was never designed to be secure, and Windows was designed primarily to be feature-rich and convenient for users. Indeed, Windows is too feature rich. Because it's meant to be all things to all people, it contains far more networking capability than home users need. And because so many components are deeply integrated with the operating system kernel, there are many superfluous and insecure features that can't be disabled without affecting other, desirable ones.

There is a tremendous amount of legacy code in Windows and other Microsoft applications, written years ago when security was the least of the company s concerns, and this code is a constant obstacle to security, privacy, and data hygiene. Bad legacy code can be likened to bad genetic material and its consequences to hereditary disease. Thus we can say that new versions of Windows and MS applications are plagued by the digital equivalent of hereditary birth defects. Windows is also quite obscure, with many hidden functions. It's often difficult for a user to observe system processes and understand their purpose. Windows frequently reaches out to the Internet without invitation and in ways that users don't anticipate, and it even quietly phones home to Microsoft on occasion. This lack of system transparency is a security challenge in itself.

Another problem with Windows comes not from Redmond but from the thousands of closed-source applications and utilities written for it, many of which have serious security holes. Indeed, some of them, especially "free" applications supported by advertising on your desktop cross the line into malware. These programs can track users across the Internet and help advertisers develop marketing profiles of people as they go about their business on line.

Yet another problem is the very architecture of Windows: it is highly interlaced with many deeply integrated and interdependent components. The alternative to this engineering scheme would be a modular architecture such as one finds in UNIX, BSD, and GNU/Linux. UNIX, as well as Linux and BSD, which share much in common with it, is designed so that a security vulnerability in one component will not typically extend into another. Vulnerable processes can be isolated, shut down if necessary, and patched without fuss. But because Windows is so interlaced and its many components so interdependent, shutting down a vulnerable process may cause system instability or even a crash.

This complex architecture also makes the operating system tricky to patch when security vulnerabilities are discovered, leaving Windows users at a disadvantage. For example, in July of 2003 Microsoft discovered that a service called RPC (remote procedure call) was vulnerable to a buffer overflow, which can yield complete ownership of a Windows system to a remote attacker. Three weeks after the vulnerability was announced and a patch issued, the MSBlaster worm was launched, exploiting RPC through another service called DCOM, and automatically infecting millions of Windows systems.

RPC allows a program running on one computer to execute code on another. This can be useful, particularly for networked machines sharing a hardware device like a printer over a LAN (local area network), say. However, there is no reason why any computer should run RPC if it is not supplying services to other machines on an internal network. Computers primarily meant to access the Internet should always have RPC disabled because many exploits against it have been discovered over the years. Unfortunately, RPC is deeply integrated into the Windows operating system and cannot be disabled safely: scores of other Windows components depend on RPC to function. On the other hand, users of UNIX, BSD, and Linux can disable RPC if they don't need it, because on those more modular systems RPC is an isolated service running on top of the operating system kernel. RPC is an integral part of Windows, but it's not part of UNIX; it's merely a function that can be switched on and off.

It's not uncommon for Windows users to find themselves stuck with insecure system components that can't be shut off because desirable, even crucial, processes depend on them. Therefore, this book will focus primarily on securing Microsoft Windows, but it will often do so by urging security-minded users to take advantage of the many open-source applications and utilities designed to run on it.

Let's look at another example. On 12 August 2002, I reported in my daily column for The Register a serious flaw in the way the Windows Internet Explorer and Linux Konqueror browsers handle SSL (secure sockets layer) certification. SSL is the encrypted Web protocol used by e-commerce sites and banks to establish a "secure" browser session, indicated by a little padlock icon in the browser's status bar and a Web address beginning with HTTPS instead of HTTP.

A security researcher named Mike Benham had discovered a vulnerability in Internet Explorer's implementation of SSL certification and notified Microsoft before publicizing his discovery. The open-source Mozilla browser was not vulnerable, even when run on Windows; but while researching the story I did a bit of tinkering and discovered that the Konqueror browser for Linux was vulnerable.

Benham had already notified Microsoft, but my article was the first indication that Konqueror needed a fix too.Microsoft had been given a head start. One day later, the Konqueror developers integrated a fix into the CVS (concurrent versions system) tree for the latest version. On 19 August, seven days after Benham's public announcement, all previous versions of Konqueror were fixed, despite the fact that the developers had a shorter warning period than the coders at Microsoft had got. It was not until 5 September that Microsoft began issuing patches for the vulnerability, starting with Windows NT and XP. It had taken them three weeks to begin the job, and it would take them well over a month to complete it, in spite of the advance warning Benham had given them.

One might conclude that Microsoft was slowed by the sheer size of the bureaucracy associated with such an enormous company, but that would be a mistake. The Microsoft security response team is conscientious and usually pounces on published exploits as quickly as humanly possible. The delay resulted from the essential nature of Windows' architecture. The Internet Explorer browser may appear to be a stand-alone application, something, in a sense, running on top of Windows, but it's very much integrated with the operating system kernel. The broken cryptographic function that IE used for its implementation of SSL was buried deep in the bowels of Windows.

Because several other Windows components and applications used the same crypto API (application programming interface), the patch developers had to be mindful of its many uses, and the patch itself had to be tested against scores of variables. While Internet Explorer was the thing that, in this case, exhibited the risky behavior, it's more accurate to say that Windows itself was broken and needed to be fixed -- not an easy task when you're dealing with over 35 million lines of code.

On the other hand, Konqueror, like most open-source applications, really can be thought of as a stand-alone module running on top of the Linux kernel. In its case, the broken cryptographic function belonged solely to the Konqueror browser, not to Linux. Fixing it was a straightforward affair.

For yet another example, in June of 2002 a serious exploit against the popular, open-source Apache Web server, available for both Linux and Windows, was revealed by a security vendor called Internet Security Systems (ISS). The company posted their discovery to the BugTraq security mailing list without knowing the full extent of the flaw, and without giving Apache.org time to investigate and develop a patch or even propose a workaround. To sugar the pill, ISS had developed its own patch, which Apache later said didn't address all the issues. Clearly, ISS was more concerned with taking credit for the discovery than mitigating the risks associated with it behavior all too common within the "security community" and this left the developers at Apache.org in a lurch. Nevertheless, they were able to issue fully patched versions within 24 hours.

Why? Because the Apache Web server, unlike its Microsoft counterpart, IIS (Internet Information Server), is a stand-alone application developed for several platforms. Only it needed fixing, not the operating systems that run it. This provided a clear advantage to users running Apache on Windows; the lack of deep integration with the operating system made patching the application far easier than it might otherwise have been.

The open source approach to development encourages modularity. Applications are designed in a more platform-independent manner so that they can easily be ported to numerous operating systems. This discourages deep integration with any single operating system, and so simplifies patching and upgrading. In contrast, Microsoft applications are designed for one platform only: Windows. In addition to the security disadvantages of deep integration between an application and the underlying OS, this approach also increases consumer costs by supporting vendor lock-ins that require users to buy additional software that they may not want.

There is another advantage to the modular approach of open-source applications. No matter how hard the security team at Microsoft works to ensure that a patch is safe to use, occasional problems necessarily arise whenever one is dealing with such a complicated, deeply interdependent system as Windows. Bad patches do come along from time to time, and for this reason professional system administrators (sysadmins) never install one on a mission-critical system without first installing it on a test system. In spite of the efforts made to ensure compatibility, Microsoft has at times been forced to recall patches. Thus it's not unusual for Windows admins to neglect patches entirely and seek their own workarounds to the security vulnerabilities they're meant to address. Windows is a complicated beast, and Microsoft can't possibly test every patch against every possible system configuration.

Here again, because open-source applications are generally modular in design, a bad patch stands less chance of damaging the system than one designed for Windows. Generally, it will affect only the application to which it corresponds; if a patch is flawed, it's unlikely to cause a system failure. Of course, patches must always be tested before integration into mission-critical systems, but users of UNIX, BSD, and Linux, and users of open-source applications for Windows, have less to worry about than strict MS-only users. This is simply true by design.

With this in mind, let's take our first practical step toward improving online security by installing and configuring the free, open-source Mozilla Web browser and e-mail client on Windows.

Why Mozilla?

There are many reasons why Mozilla is a better choice for the security-conscious user than Internet Explorer and Outlook Express. We've already touched on one reason: it's not integrated with Windows, so security issues can be addressed quickly and with little danger of causing wider system difficulties. Also important is the simple fact that it's open source and therefore transparent: anyone is welcome to review the source code and see for himself exactly what it does and how it works. There are no secrets in Mozilla.

On the other hand, Internet Explorer and Outlook Express (and Netscape and Opera) are closed-source products. Microsoft doesn't permit consumers to look under the hood, so to speak. All we know about these products is what's stated in the documentation, but Microsoft has for decades included undocumented functions in many of its products. Obviously, any software containing secret functions is an obstacle to good security.

Furthermore, the Mozilla browser offers users more control over potentially risky features like Java and JavaScript. It doesn't run ActiveX controls, a dangerous gimmick with which Microsoft is much enamored. It offers superior user privacy with better management of the URL history, page cache, cookies, plugins, and passwords. Even better, the Mozilla e-mail client can be configured to display messages in plain text rather than HTML (hypertext markup language), perhaps the single most productive step a user can take toward online security. Or, said another way, allowing HTML rendering and scripting in e-mail is one of the most common risky habits. It is not HTML per se that's at issue; it is, rather, the scripting support in HTML rendering engines (the programs that cause HTML to display as it was intended) that allows malicious code in e-mail memos to run, even when the recipient takes no action. Such scripts can cause major system compromises, allowing an attacker to take over a victim's machine. The deeper the integration of the Internet client into the operating system, the more dangerous these scripts can become.

Microsoft's solution has been to issue patch after patch, fixing each type of scripting vulnerability individually as it becomes known. You can see the problem here: the flaw has to be known before it can be addressed, but of course the blackhat community likes to keep its discoveries and exploits secret for as long as possible. Yet Microsoft has for years refused to allow users to employ the simplest and most effective solution to scripting vulnerabilities whether they're known or unknown: to shut off HTML rendering and scripting support in their e-mail clients.

After all these years of difficulty, Outlook Express and Hotmail didn't receive HTML "off switches" for incoming mail until the summer of 2003, while Outlook is, at this writing, not scheduled to get its own until the next release. Why the company should have demanded for so many years that HTML formatting be displayed in e-mail, whether the user wishes to see it or not, is open to speculation. It could be that Microsoft feared that users would be disappointed in the look and feel of their e-mail if it should fail to throb with color advertisements, pornography, and clever animations. Or it could be that the company has a quiet financial interest in accommodating the direct-marketing industry, which wants its torrents of spam to be as eye-catching as possible.

Even the simplest HTML elements, like an image to be fetched off the Web and displayed in your e-mail, can give spammers the confirmation they need that your address is valid, even if you delete the message immediately after it arrives. A tracer image can be hidden in the HTML code and fetched automatically from a remote server in such a way that a unique identifier -- possibly as simple as your e-mail address -- will be logged along with your IP address for later harvesting as a known, valid contact. By the time the image appears, you have, in a very real sense, already replied to the message and the spammer has got your number, so to speak.

Turning off HTML prevents dangerous scripts from running. It also reduces spam because your e-mail address can't be verified unless you take deliberate actions, like replying to the message or following the link provided to remove yourself from the spammer's list. Often, the removal links are a scam designed to confirm your address in case you're smart enough to disable HTML, so you should never follow them.

For an added, and significant, bonus, an HTML-off setup for e-mail prevents pornographic images from being fetched and displayed in spam messages that small children might encounter -- an important consideration on home machines.

Now that Microsoft has finally begun to address the security problems with HTML rendering and scripting support in their e-mail clients, the chief problems remaining are the numerous duplicate data traces that Internet Explorer and Outlook Express scatter about the system, the difficulty of removing them, and the integration of these applications into the low-level realm of the Windows operating system, where risky client behavior can lead to radical system difficulties.

Fortunately, Windows users can employ numerous workarounds, and, where necessary, side-step such problems altogether. Accordingly, replacing a number of MS clients with safer and more transparent open-source substitutes is a crucial bit of housekeeping that this book will explain and encourage throughout. As Internet Explorer and Outlook Express can't be made secure enough, no matter how hard one might try to overcome their shortcomings, we will simply bypass these problems by installing Mozilla in their place.

NOTE: Mozilla Mail is a superior replacement for Outlook Express, but hardly an adequate one for MS Outlook. Readers looking for a safer alternative to Outlook should check out Ximian Evolution, a free, open-source Outlook clone that's fully compatible with MS Exchange. Unfortunately, it's available for Linux and Solaris only. Windows users who can't do without Outlook are stuck with it for now.

Getting Mozilla

The first step is to point your browser to Mozilla.org and find the latest stable release for your operating system. You will find it linked on the home page. If you're not a power user, don't download any of the release candidates, indicated by the initials RC in the file name. If you are a power user, then by all means feel free to experiment with the newest, bleeding-edge candidate. Otherwise, stick with the most recent stable build.

The file you will download first is the Mozilla installer; this will take only a few minutes on a fast connection. You can then run it as you would any Windows installation wizard. If you are new to Mozilla, when you reach the "Setup Type" dialog you should select the "Complete" option. In the next dialog, you will be asked if you want to use the Quick Launch feature. This helps Mozilla launch rapidly, the way Internet Explorer does, by preloading it at boot time. There is no harm in selecting this option.

Next, you will be invited to save the installation files in case you should wish to reinstall the current version of Mozilla without downloading it again. Broadband users needn't bother, but 56K-ers might wish to choose "Yes." You will also be given an opportunity to configure your proxy settings if your ISP requires you to use one, though this can be dealt with later, using the browser's Preferences menu if you wish. Users not required to use a proxy may ignore this setting for now, though we'll be learning a great deal about proxies, and how to use them for online privacy, in Chapter Five.

Mozilla will be ready to use without a reboot, which is a good sign because this means it doesn't depend on the Windows Registry, a mysterious complex of data files that is read at boot time, where other browsers and Web-enabled applications may leave data traces indicating your online comings and goings. For example, URLs (universal resource locators) -- that is, Internet addresses that you type into the address field of Internet Explorer -- are recorded in the Registry, along with numerous other bits of potentially sensitive personal data that ought to be under your control but are not, such as a list of the files you've searched for on your hard drive, files you've accessed recently, and several other items that we'll learn about in due course.

When Mozilla has finished installing itself and pops up on your desktop, you will be asked one more thing: whether you want it to become your default browser. I recommend that you make it so. But you should not remove or disable Internet Explorer because you'll need it for Windows Update (though I would not recommend using it for any other purpose).

Now it's time to set up the mail and news client. You can launch it from the Mozilla browser by going to the menu bar and selecting Window ==> Mail & Newsgroups. But let's make a desktop icon for it instead. From the Windows desktop Start Menu, go to Programs ==> Mozilla ==> Mail. Right-click on the Mail icon and drag it to the desktop. When you activate it, a setup wizard will start, allowing you to enter your account information just as you would in setting up Outlook Express. Again, you will be asked if you want to make Mozilla your default mail client, and again I recommend that you do just that.

Secure Configuration

You've now got a Web browser and an e-mail client that you can configure for security considerably better than the disappointing baseline levels established by Internet Explorer and Outlook Express. Only you do have to configure them. What follows is a walk-through of the various settings and available options with recommendations for improving online security, data hygiene, and user privacy, with accompanying screen shots of the correct settings. Fortunately, Mozilla is a good deal simpler to configure than Internet Explorer, with all of its confusing "zones" and individual permissions, most of which are easily exploitable with malicious scripts anyway. Most, though not all, browser exploits affect Internet Explorer exclusively; and most, though not all, e-mail worms affect Outlook and Outlook Express exclusively, so merely replacing them with the Mozilla browser and mail client will protect you from a host of online threats. But there are a number of tricks to make Mozilla even more secure, so let's go through them one at a time.
[....]

HomeIntroductionReviewsToolsUpdatesPurchaseContact